
SECURITY TESTING
Find exploitable vulnerabilities before attackers do
Combine AI, automated scanners, and certified pentesters in one continuous security program that finds exploitable vulnerabilities across your code, apps, APIs, and cloud, then verifies every fix.

How we test your software
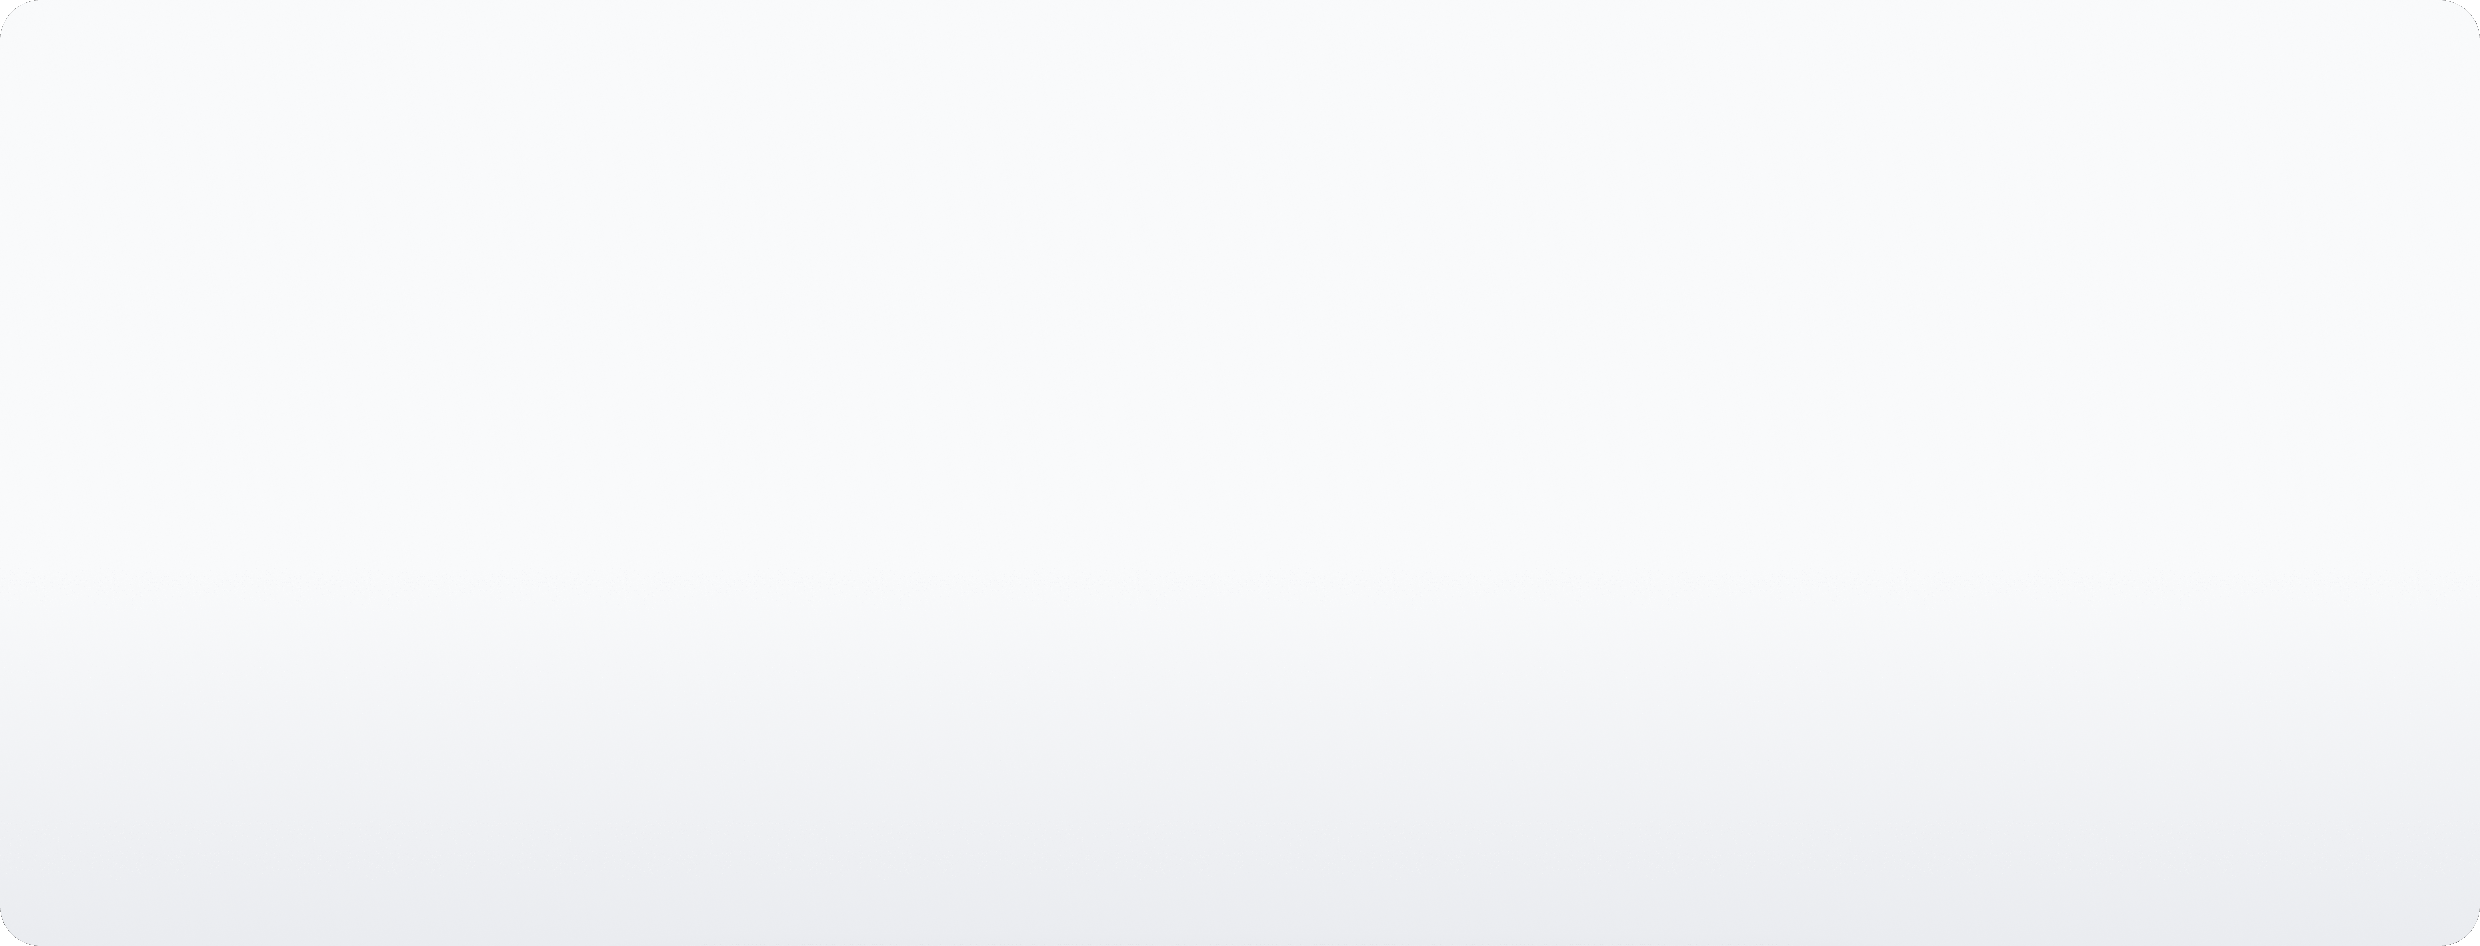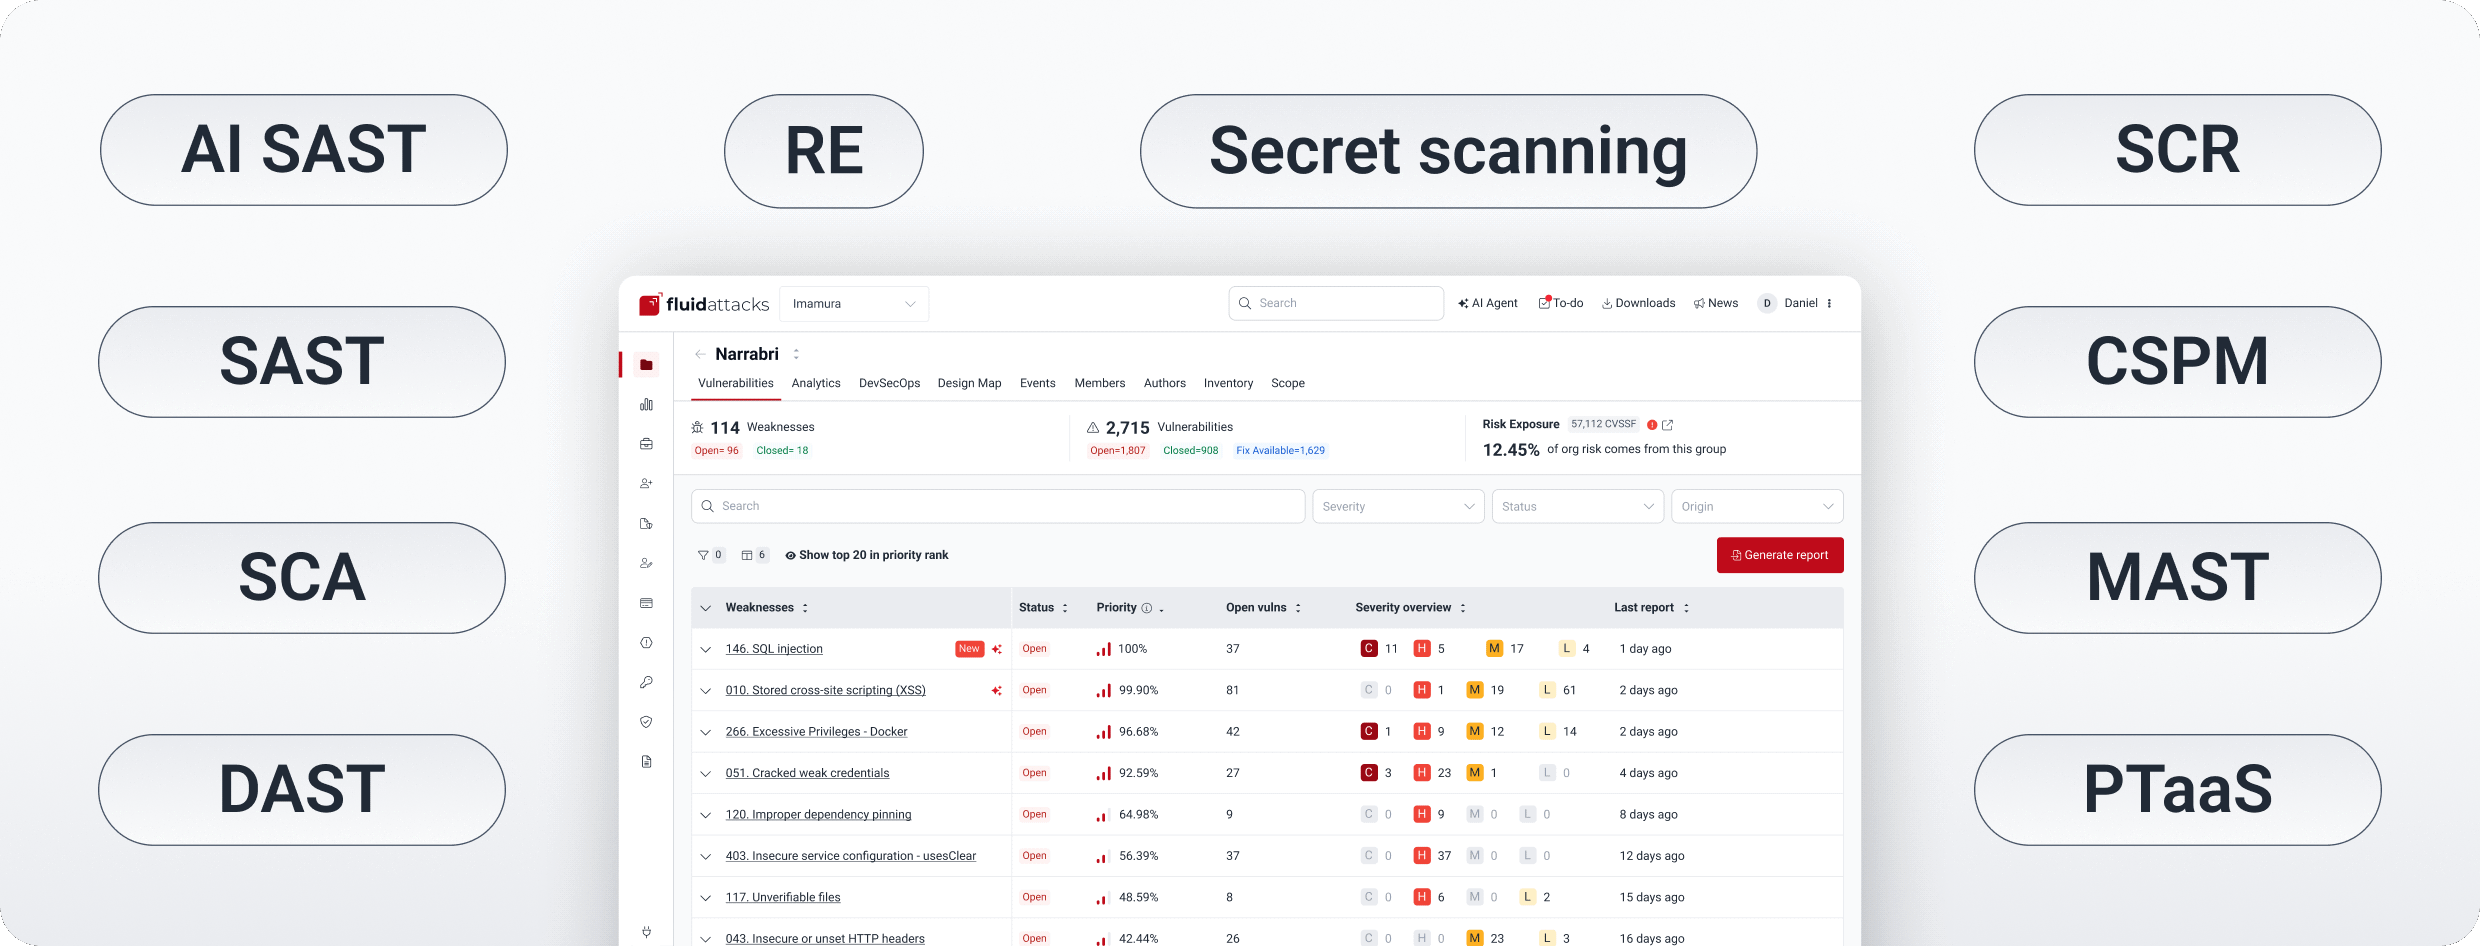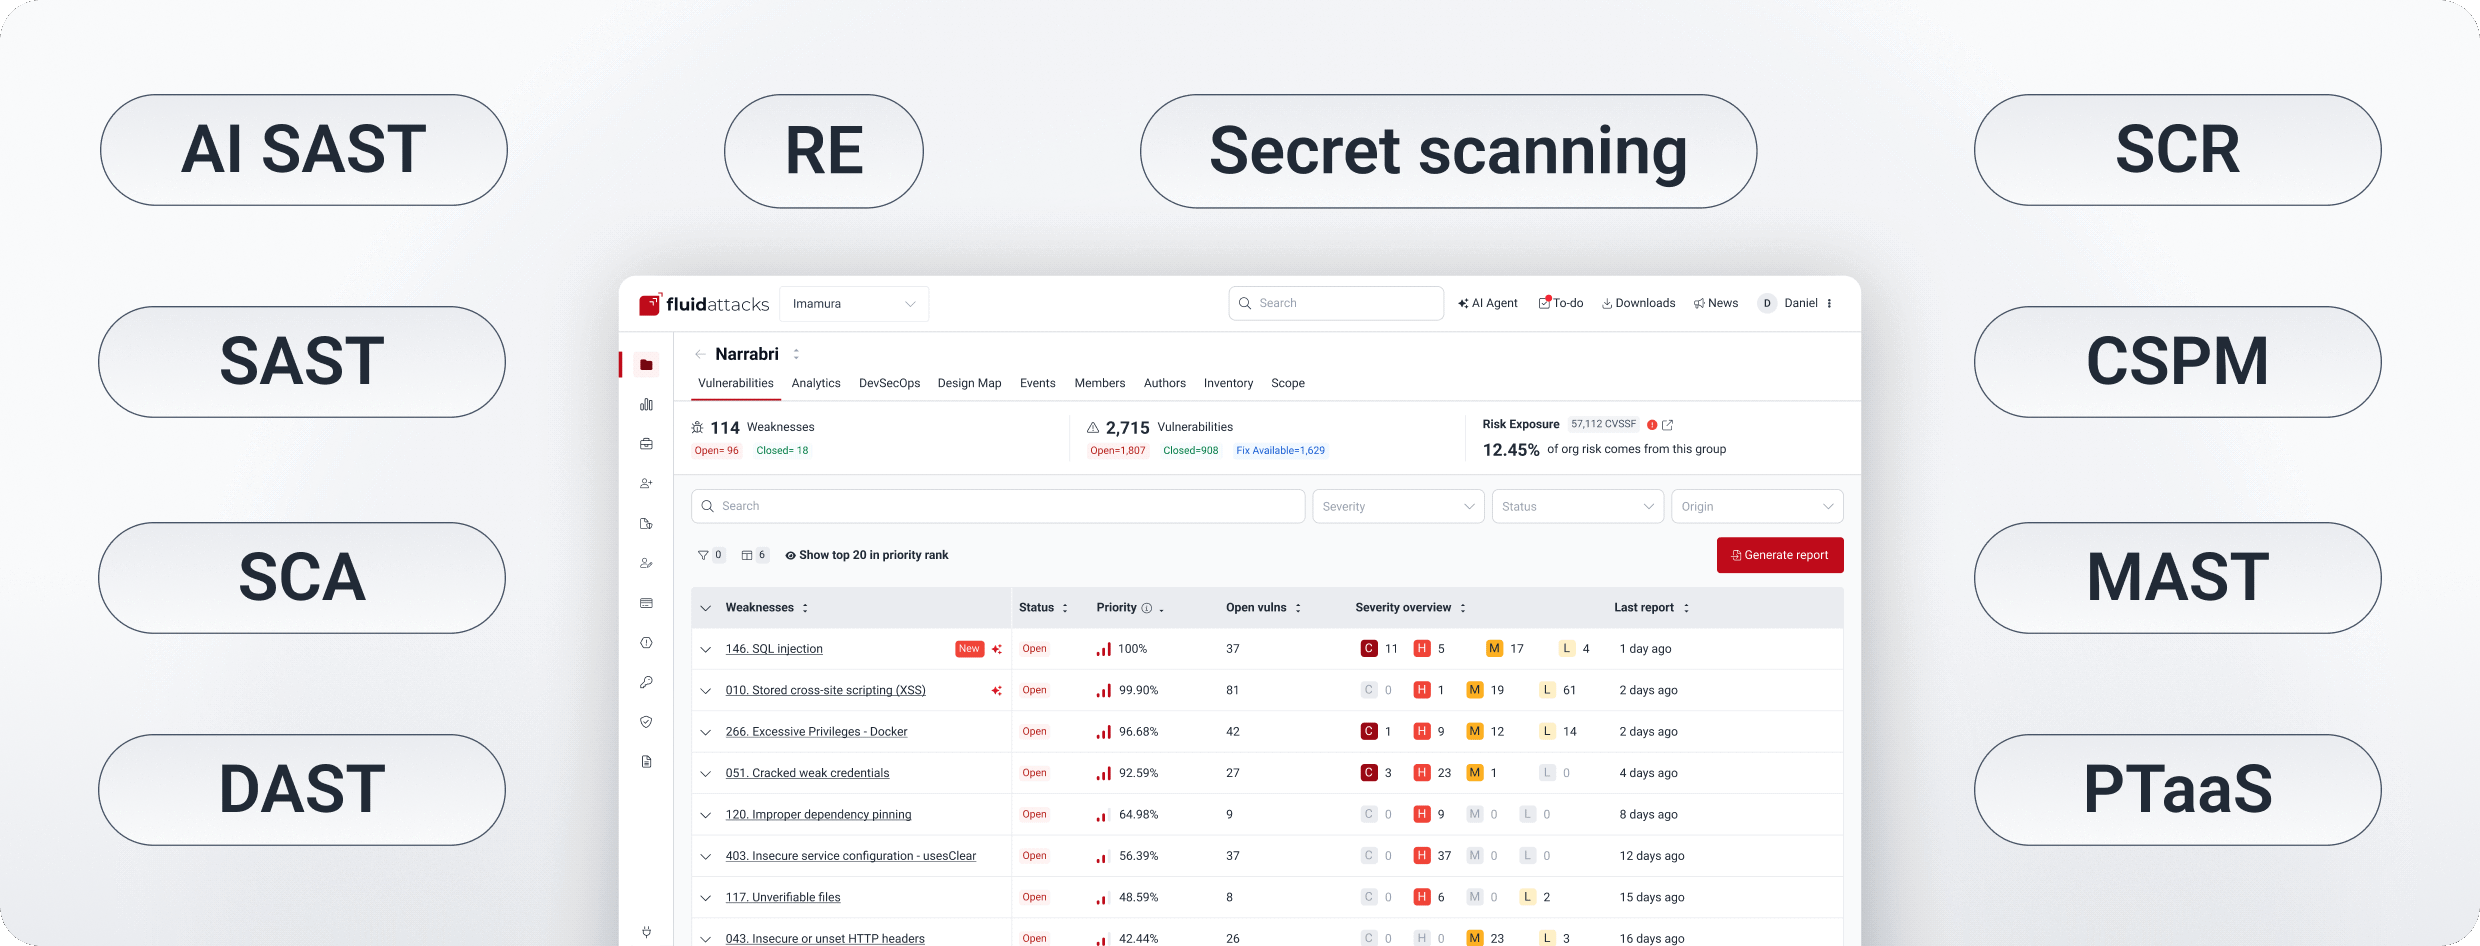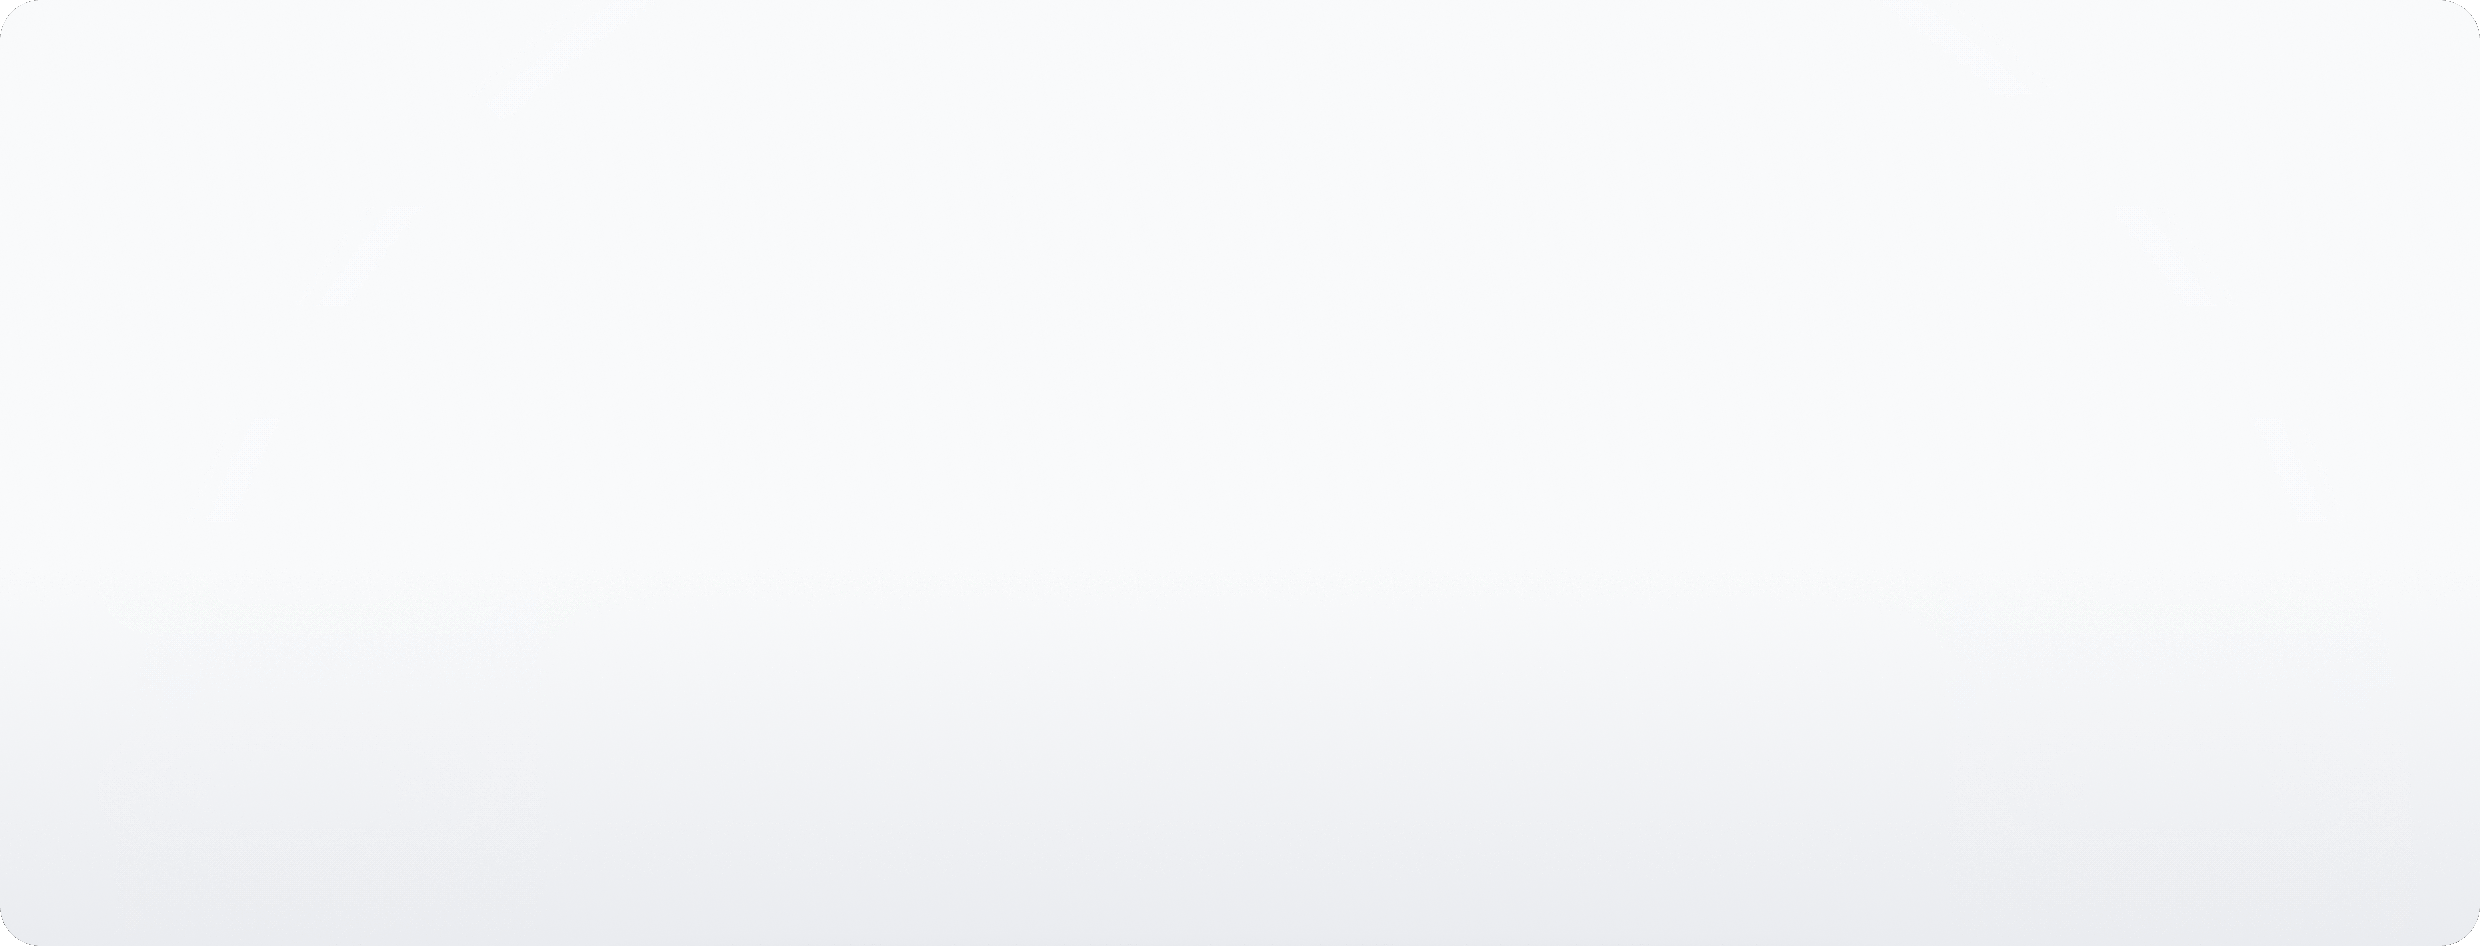
We assess your code, running apps, and cloud as a real attacker would, combining automated and manual techniques at every layer.
Analyze your source code
SAST, AI SAST, SCA, and secret scanning flag insecure patterns, vulnerable dependencies, and exposed secrets. Our pentesters then validate real risks through manual secure code review.
Attack your running apps
DAST and MAST scan web apps, APIs, and mobile apps. Through PTaaS, our pentesters exploit business logic and authorization flaws and reverse engineer mobile binaries.
Review your cloud infrastructure
CSPM checks identity policies, storage permissions, and network rules to catch the misconfigurations behind real breaches.
[ KEY BENEFITS ]
Why tools alone aren't enough
Tools give you breadth. Pentesters find the critical issues tools can't reach. Our own research shows how big the difference is.
Find what scanners miss
In our benchmark, pentesters alone reported 86.8% of the total risk exposure.
Catch the critical issues
In 2025, our pentesters detected 90% of the risk exposure from critical vulnerabilities and reported five times more risk per vulnerability than tools.
Trust every finding
Our pentesters reported zero false positives in the benchmark, so your team spends its time fixing, not triaging.
Rely on certified pentesters
Our pentesters hold more than 60 offensive security certifications, covering web, mobile, cloud, red teaming, and exploit development.
Work with a top-ranked team
Our pentesting team finished #9 worldwide and #1 in Latin America in the 2025 Hack The Box Business CTF.
Count on proven vulnerability research
Fluid Attacks has been a CVE Numbering Authority since 2021 and ranks among the top 10 CVE labs worldwide, disclosing vulnerabilities in third-party software.
Explore our testing capabilities


One continuous security loop
From prevention to remediation.
SUPPORT
Security testing is a core part of our solution
We offer an all-in-one solution that combines our platform, AppSec tools, AI, and our team of pentesters to help you continuously improve your cybersecurity posture.













