Ekia File Manager 1.2.7 - Exported ContentProvider allows unauthorized file access
8,5
High
Discovered by

Offensive Team, Fluid Attacks
Summary
Full name
Ekia File Manager 1.2.7 - Exported ContentProvider allows unauthorized file access
Code name
State
Public
Release date
Affected product
File Manager
Vendor
Ekia
Affected version(s)
1.2.7
Vulnerability name
Unauthorized access to files - APK Content Provider
Vulnerability type
Remotely exploitable
Yes
CVSS v4.0 vector string
CVSS:4.0/AV:L/AC:L/AT:N/PR:N/UI:N/VC:H/VI:H/VA:N/SC:N/SI:N/SA:N
CVSS v4.0 base score
8.5
Exploit available
Yes
CVE ID(s)
Description
Ekia File Manager 1.2.7 exposes com.ekia.filecontrolmanager.OpenFileProvider as an exported Android ContentProvider without requiring caller permissions.
The provider maps the caller-controlled URI path directly to a filesystem path and passes it to new File(...). It then supports query(), openFile(), and delete() operations. Because the provider is exported and lacks android:permission, android:readPermission, or android:writePermission, another local application can access the provider authority and cause File Manager's process to read, create, overwrite, or delete files that are accessible to that process.
The issue allows an unprivileged local application to cross an Android app boundary and abuse File Manager's storage access as a confused deputy. Impact depends on Android version, granted storage permissions, and the targeted path, but the validated code path supports unauthorized confidentiality and integrity impact.
Vulnerability
Root cause
The provider is exported without access-control permissions. The APK manifest declares:
No android:permission, android:readPermission, or android:writePermission is present on the provider declaration.
The provider accepts only the authority as an authorization condition.
OpenFileProvider.g()returns true solely when the URI authority equals com.ekia.files.manager.files:
The provider converts the caller-controlled URI path directly into a file path.
OpenFileProvider.c()returnsuri.getPath()without canonicalization, allowlisting, or root-directory restriction:
The provider exposes write-capable file modes.
OpenFileProvider.h()maps caller-supplied modes includingw,wt,wa,rw, andrwttoParcelFileDescriptorflags.The provider opens files using the unrestricted path.
openFile()constructs new File(c) from the URI path and returns a ParcelFileDescriptor:
The provider exposes deletion using the same unrestricted path.
Source-to-sink path
Source: the unauthenticated attacker controls the destination filename query parameter in a URI addressing the exported authority
content://com.ekia.files.manager.files/...Authorization gate: none; Android routes the request to OpenFileProvider because
android:exported="true"and no provider permissions are required.Controller:
OpenFileProvider.c(uri)returnsuri.getPath()for any URI with the matching authority without validating that it stays inside an approved directory.View:
openFile()passes that path to newFile(...)andParcelFileDescriptor.open(...)using a caller-supplied mode.Browser sink:
delete()passes the same path to newFile(...).delete(), allowing critical system or external storage files to be selected.
Impact
Successful exploitation allows a local attacker application to cross an Android app boundary and abuse File Manager's storage access as a confused deputy, leading to unauthorized read, creation, overwrite, or deletion of files that are accessible to the provider process.
PoC
Preconditions
Ekia File Manager 1.2.7 is installed.
The target file is accessible to the File Manager process.
For shared external storage paths, impact depends on Android version and the storage
permissions/all-filesaccess granted to File Manager.No attacker authentication, app-specific permission, root, or user interaction is required for provider calls.
Reproduction
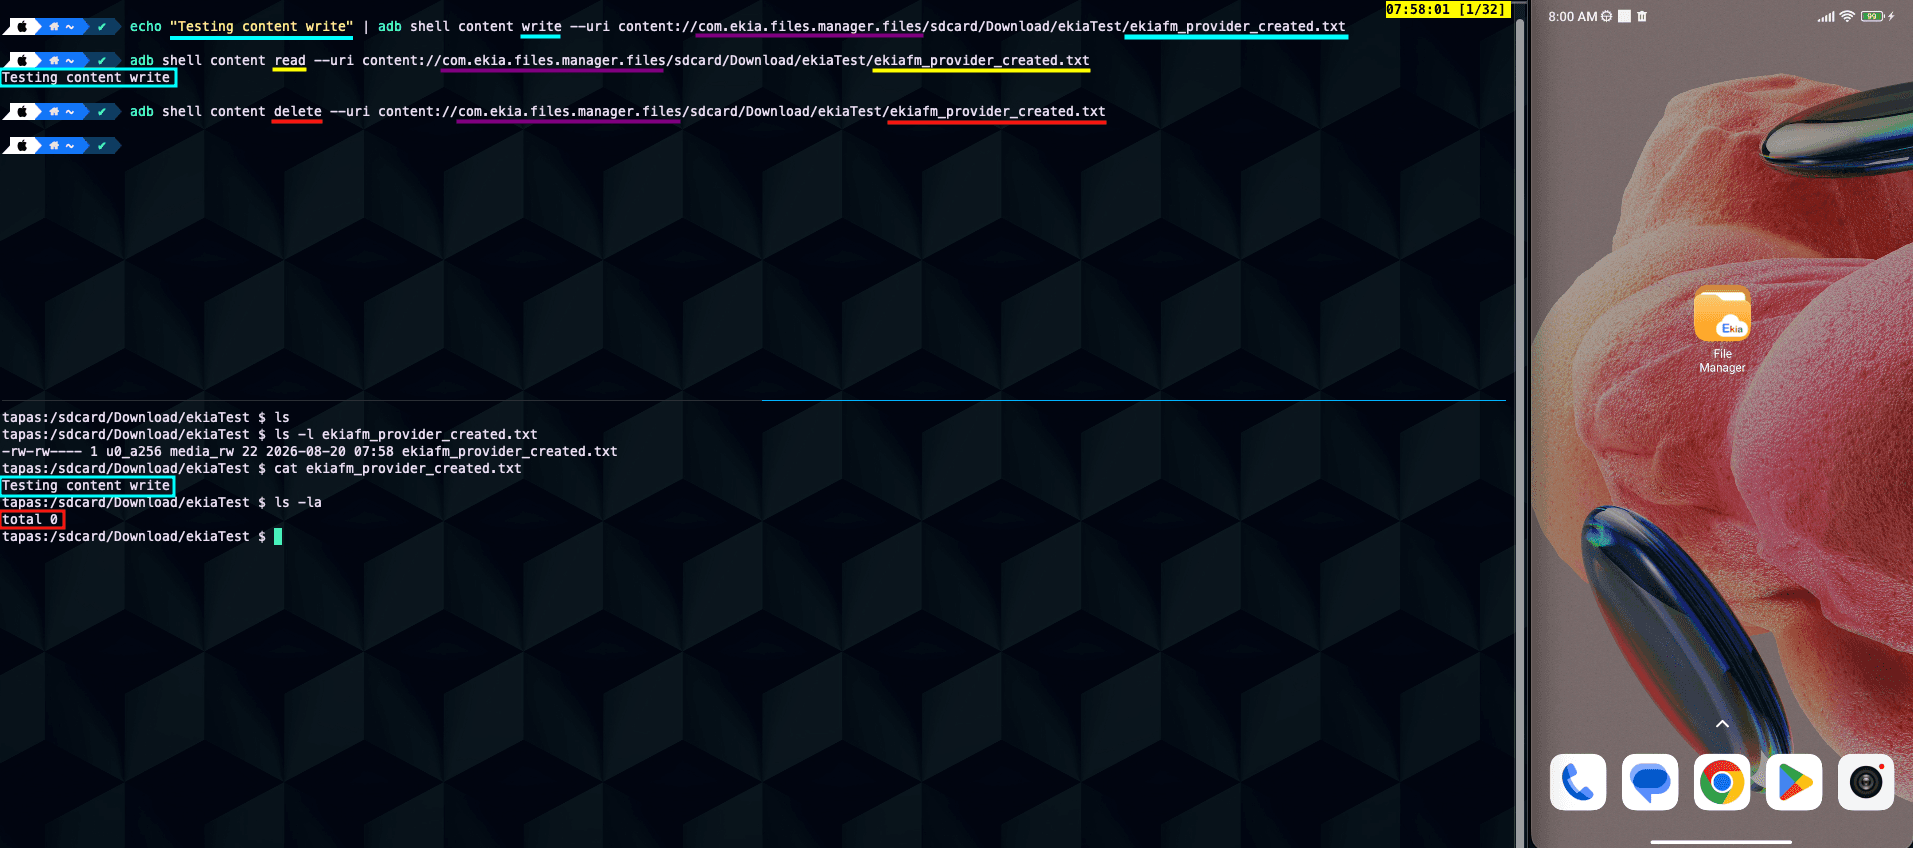
Create a benign test file in shared storage:
Read the file via the exported provider:
Expected result:
Create or overwrite a file through the exported provider:
Verify the result:
Delete a file through the exported provider:
Expected result:
The file is deleted by the provider process.
The caller did not need a File Manager-specific permission or URI grant.
Evidence of Exploitation
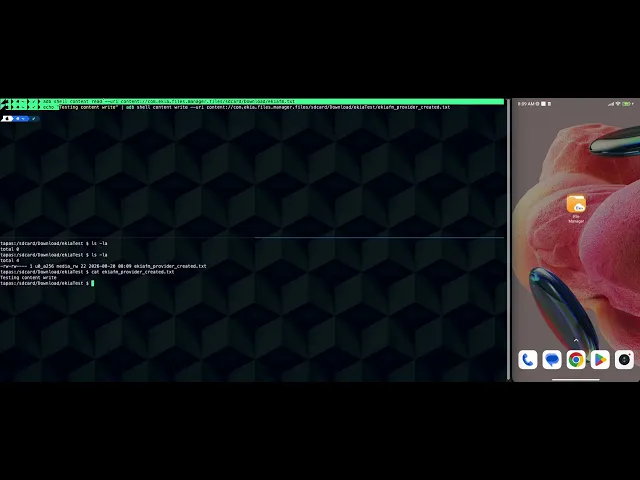
Video of exploitation:
Static evidence:
Our security policy
We have reserved the ID CVE-2026-81301 to refer to this issue from now on.
System Information
Ekia File Manager
Version: 1.2.7
Operating System: Android 5.0 and up
References
Mitigation
There is currently no patch available for this vulnerability.
Credits
The vulnerability was discovered by Andrés Ramos from Fluid Attacks' Offensive Team.
Timeline
Vulnerability discovered
Vendor contacted
Public disclosure
Does your application use this vulnerable software?
During our free trial, our tools assess your application, identify vulnerabilities, and provide recommendations for their remediation.